AWS explains AgentCore memory path for Bedrock agentic retrieval
AWS has documented how AgenticRetrieveStream restores short-term session history, searches long-term AgentCore memory and saves new exchanges, while developers remain responsible for identity, routing and access control.
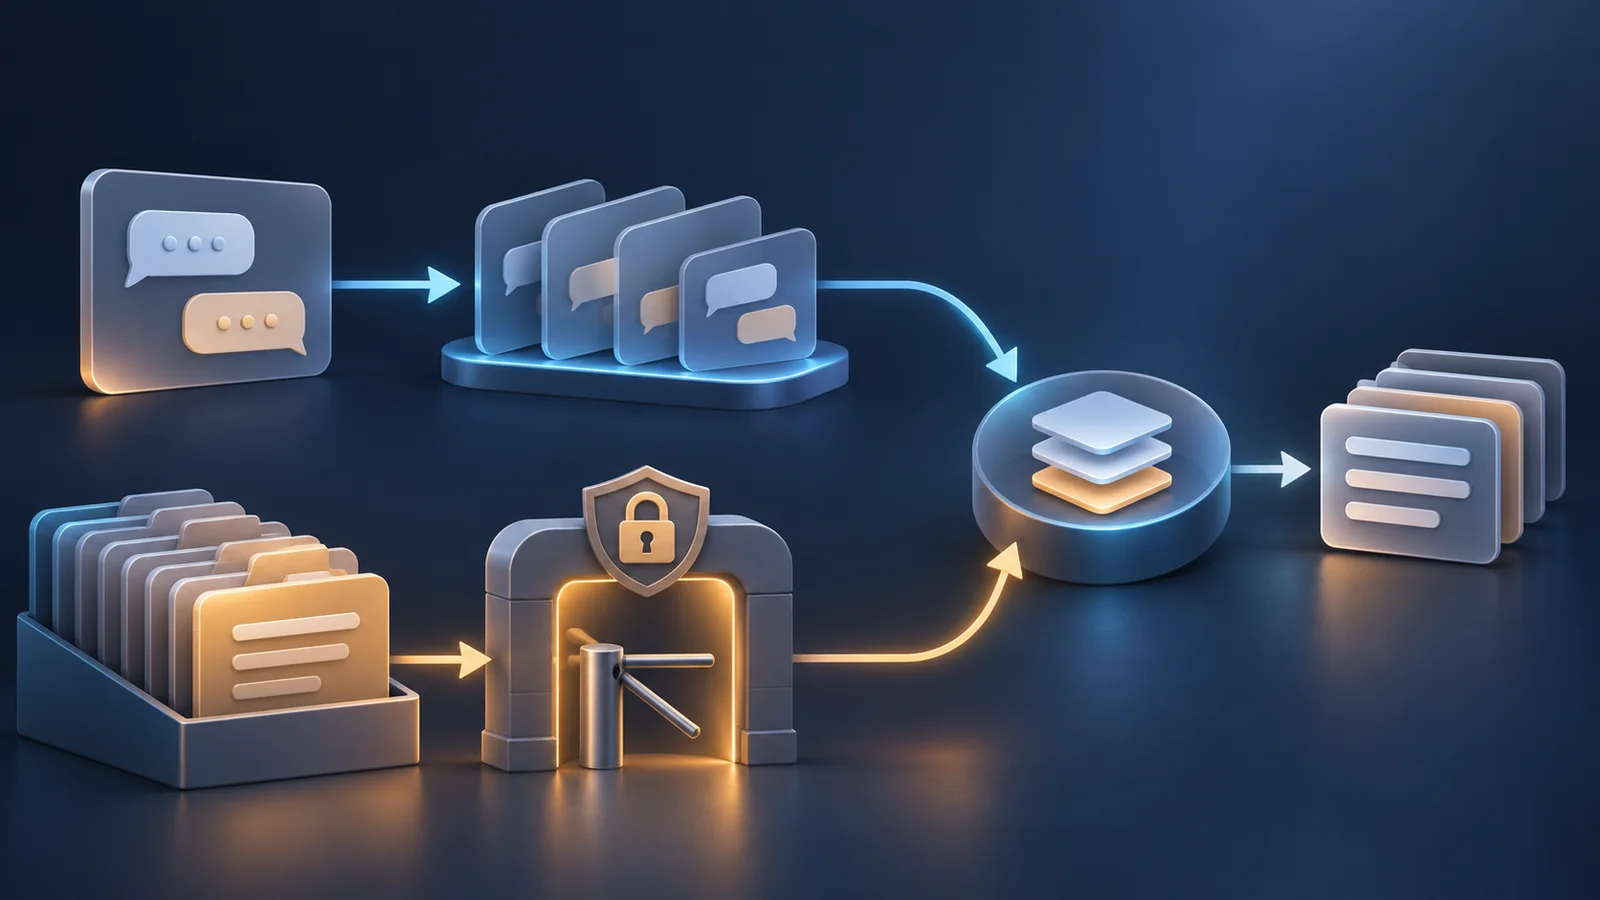
AWS has published a guide to connecting AgentCore Memory with AgenticRetrieveStream. The setup gives Amazon Bedrock Managed Knowledge Base applications a managed path to restore a conversation, search memory extracted from earlier sessions and save a new exchange. Applications still must authenticate users and supply the correct identity, session, namespace and IAM context.
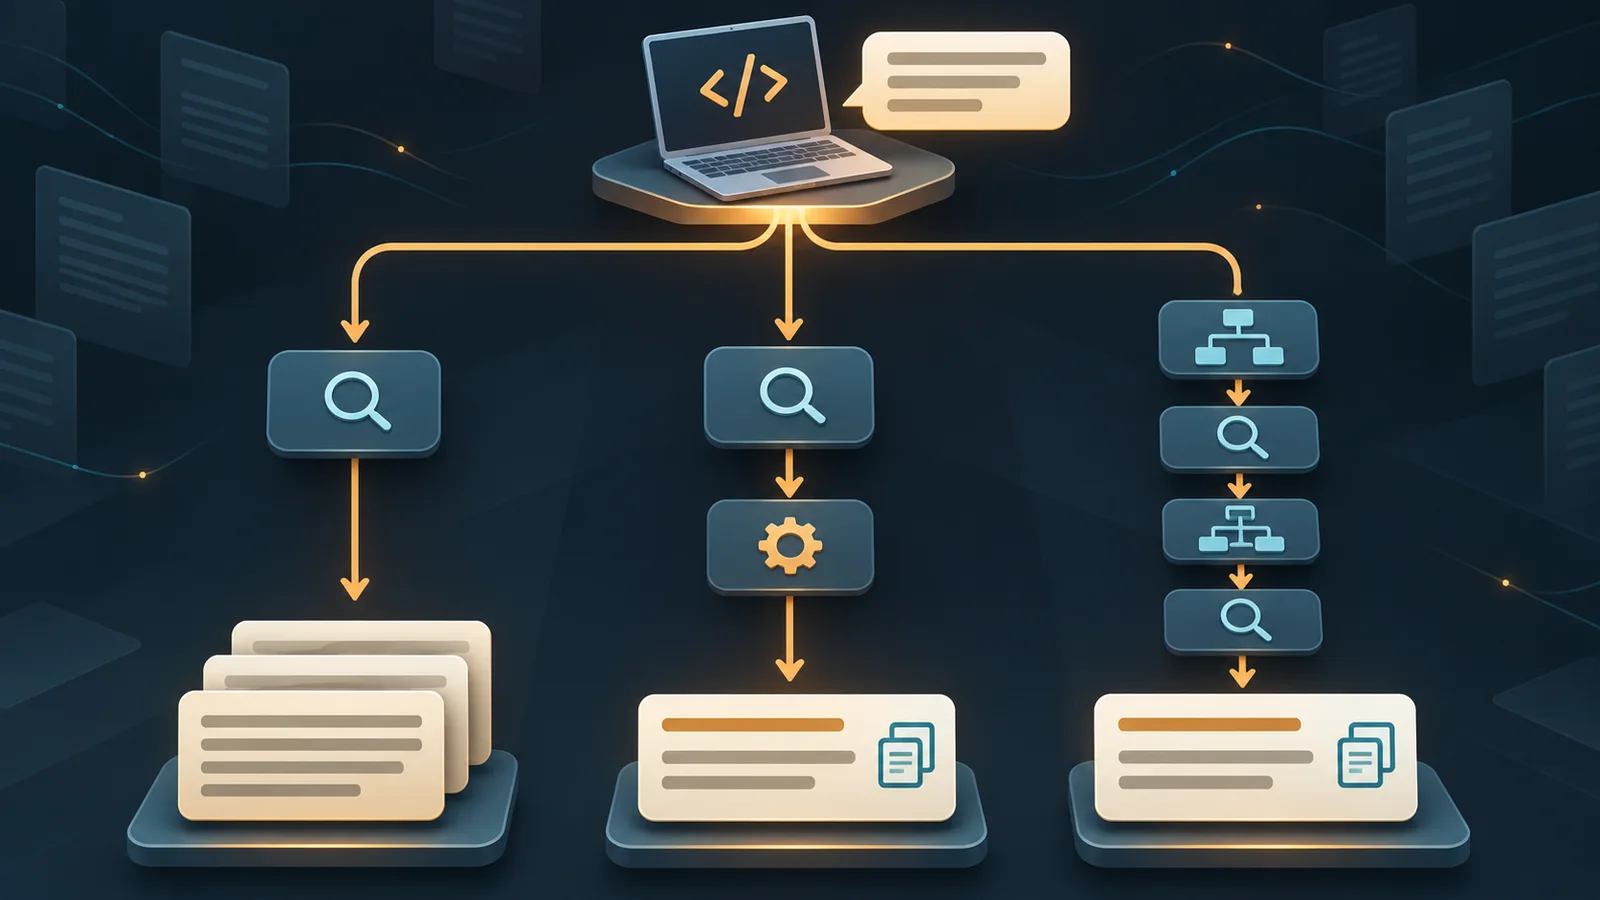
Developers enable memory through the optional memoryConfiguration object in Bedrock’s AgenticRetrieveStream request path. AWS’s request documentation says the object must include an active AgentCore memoryId and at least one of two paths: sessionBinding for short-term memory or retrievalConfigs for long-term memory. A memory ID by itself is invalid.
For short-term memory, actorId and sessionId restore earlier user and assistant events before the retrieval agent starts planning. When sessionBinding is present, the request’s messages field can contain only the current user query; callers cannot include the earlier transcript in the same request. AgentCore defines an event as the basic unit of short-term memory, organized by actor and session.
Long-term memory exposes records that AgentCore extracted from previous sessions. A retrieval configuration points to a resolved namespace or a parent namespacePath, with optional strategy and metadata filters. The retrieval agent decides whether to search that memory and writes the search query. AWS describes namespaces as hierarchical paths that can separate records by actor, session, strategy, tenant, team or environment.
With a session binding active, persistenceMode determines what happens after the response. The default mode writes the current question and generated answer back as one event and requires response generation to be enabled. Setting the mode to NONE restores history without changing the session.
None of those managed steps verifies that a request belongs to the intended user or conversation. AWS says applications must supply the correct memory ID, actor, session binding and namespace values; wrong values can return unexpected results. Namespace isolation also depends on normalized paths and correctly scoped IAM policies. AWS documents condition keys for exact namespace and namespace-path access, including the leading and trailing slashes required for policy matching.
Document permissions are a separate layer. Bedrock’s ACL-aware retrieval can filter results using permissions ingested from connected data sources and a user context supplied at query time. AWS says the filter is not an authorization boundary. Bedrock does not authenticate the end user, so the application must do that and pass verified identity information instead of relying on the filter alone.
The caller also needs the base permissions for the agentic retrieval stream, knowledge-base retrieval, full-document access and model streaming. Memory adds bedrock-agentcore:GetMemory; restoring a session adds ListEvents; long-term retrieval adds RetrieveMemoryRecords; and default persistence adds CreateEvent. A customer-managed encryption key also requires kms:Decrypt. The memory resource must be active and in the same AWS account as the managed knowledge base.
The November guide is not the first record of API support. AWS’s Go SDK changelog lists memoryConfiguration support in version 1.58.0 on August 17, 2026, describing the same short-term continuation and long-term retrieval paths.
More news
AWS adds xAI’s Grok 4.7 to Amazon Bedrock
AWS releases catalog of 23 reusable generative AI assets
AWS adds single-shot and retrieval-only modes to Bedrock knowledge bases