AWS adds query-time source permission checks to Quick and Bedrock RAG
AWS says Amazon Quick’s admin-managed Google Drive knowledge bases and supported Bedrock connectors now add live permission checks after indexed ACL filtering.
AWS says it has added query-time permission checks to Amazon Quick and Amazon Bedrock Knowledge Bases. The change gives supported retrieval-augmented generation setups a second access-control step before retrieved text reaches a model.
The update concerns permission enforcement in RAG. It is separate from Amazon Quick’s Live Data in Apps update.
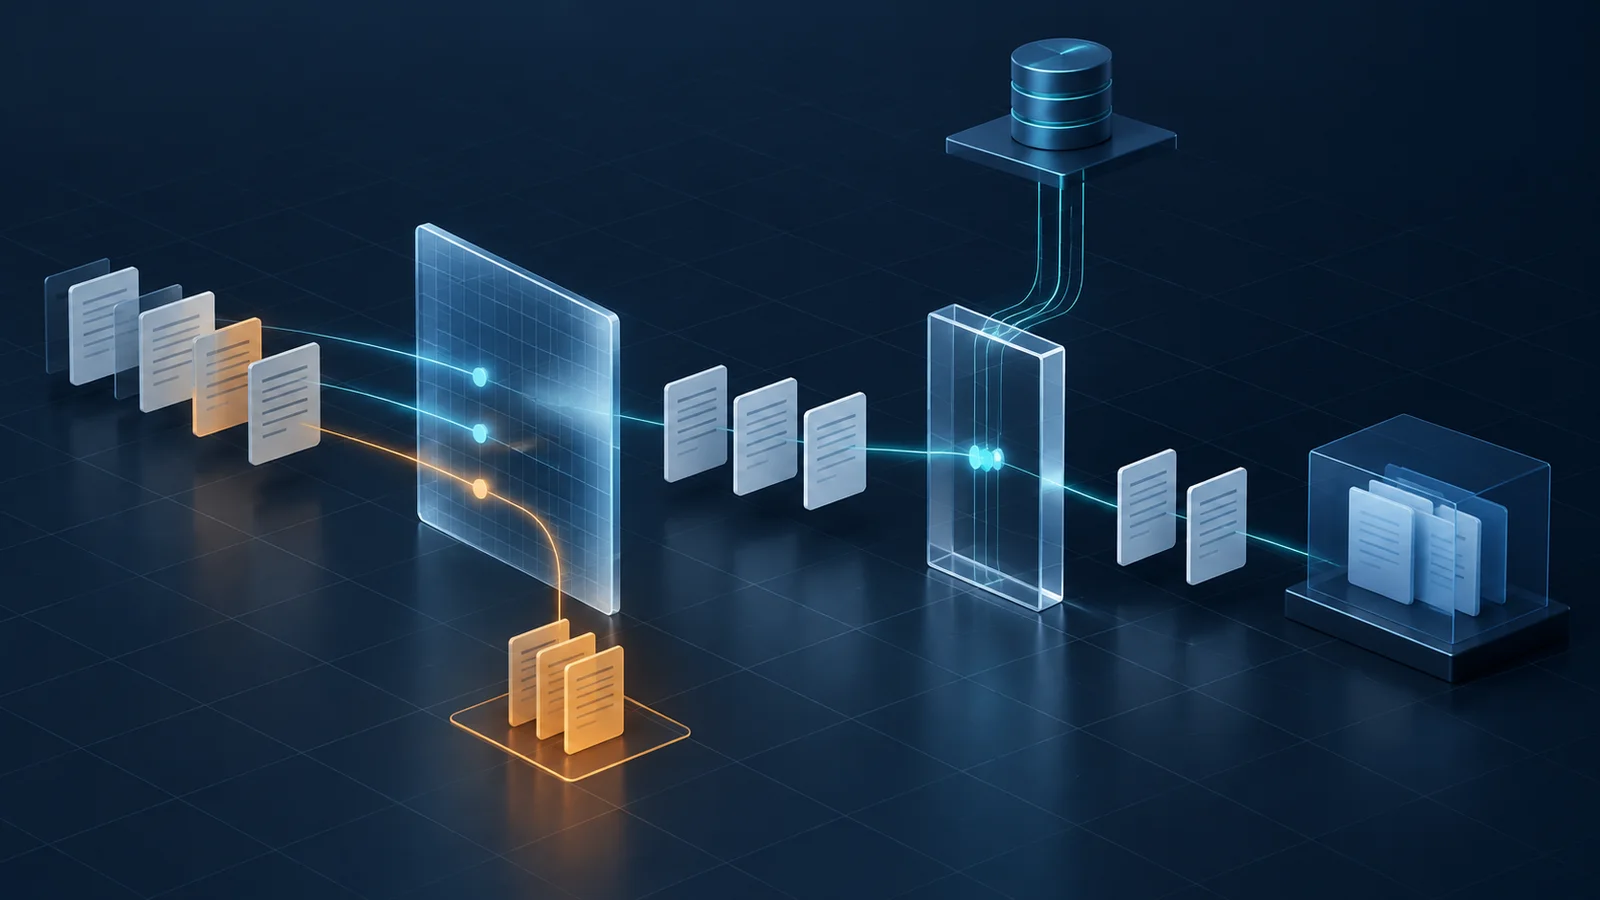
The query-time check comes after an initial filter based on access control lists, or ACLs, stored in the search index. AWS documentation says checking the source system again can catch document-permission changes made after the most recent ingestion sync, narrowing the interval in which cached permissions may be stale. AWS claims revoked access can be reflected in AI responses “within moments” rather than hours or days, but its announcement provides no benchmark or latency data for that claim.
How the two stages work
For an admin-managed Google Drive knowledge base in Amazon Quick, the first stage searches the vector index and applies its stored ACLs. That produces a smaller set of candidate documents. AWS says this avoids the cost of making a live API request for every indexed document.
Quick then calls Google Drive APIs to verify those candidates. It uses an administrator-provided service-account credential to create user-specific access tokens through impersonation. Quick removes documents the user cannot access and sends only authorized passages to the model as context. Google documents that Workspace administrators can grant a service account domain-wide authority to access user data on users’ behalf within approved scopes.
Amazon Bedrock Knowledge Bases follows the same broad sequence: stored ACLs filter retrieval results before a live source check confirms access. AWS documentation lists real-time verification support for SharePoint, OneDrive, Google Drive, Confluence and Confluence Data Center. S3 and custom connectors support the indexed filter but not real-time verification, while the web crawler does not support ACL awareness.
The Bedrock documentation also says ACL-aware retrieval is filtering, not a complete authorization boundary. Applications must authenticate users and pass verified identity context to Bedrock. AWS says the service fails closed when permission evaluation, group resolution, live verification or an internal service fails, excluding affected documents rather than returning them. Group memberships remain as fresh as the last sync, and AWS warns that ACL propagation for very large groups can lag even after a successful refresh.
More news
AWS adds GLM 5.3 to Amazon Bedrock for eligible enterprises
AWS maps Claude 5.5 access across Bedrock endpoints in GovCloud
AWS adds GPT-6.1 Sol to Amazon Bedrock