IBM launches identity and access controls for enterprise AI agents
IBM has made Agent Identity and Vault 2.2 generally available, while Secure Hub and new watsonx Orchestrate discovery and containment controls remain in preview.
IBM announced identity, access and operational controls for enterprise AI agents, drawing a clear line between products now generally available and capabilities still in preview. IBM Agent Identity, HashiCorp Vault 2.2 and watsonx Orchestrate evaluation tools are generally available. HashiCorp Secure Hub is in public preview; newly announced Orchestrate discovery and containment controls are in technical preview.
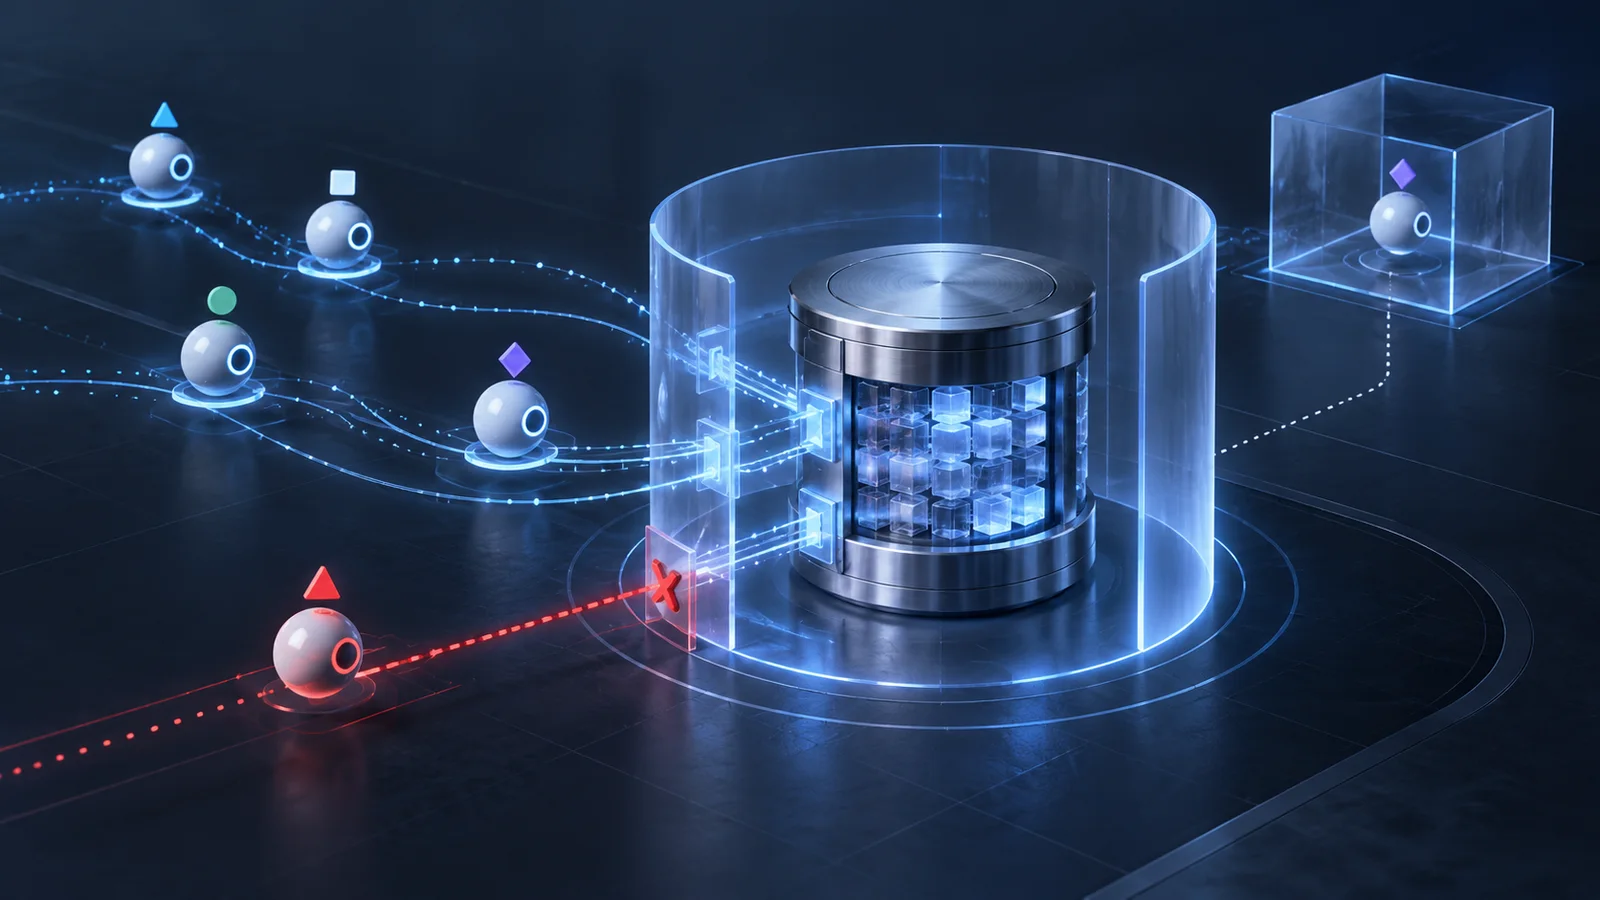
IBM says Agent Identity gives security teams a control plane to register agents, record their owners and delegated authority, apply access policies and retain audit evidence. According to the company, Vault can issue short-lived credentials for specific tasks, enforce least-privilege policies and revoke access when authorization or risk conditions change.
Vault Enterprise 2.2 is generally available with delegated authorization boundaries and task-scoped, ephemeral authorization for agents and other non-human identities. HashiCorp describes Secure Hub as a centralized view of distributed Vault environments, including operational-health, secrets and certificate information.
Release stages also diverge across the watsonx Orchestrate controls. IBM says its discovery capability, now in technical preview, can find third-party agents, models and MCP servers across Amazon Bedrock, Microsoft Foundry and Google Gemini. The containment capability is also in technical preview and includes isolated agent sandboxes and a kill switch. Orchestrate’s generally available evaluation tools support predeployment testing, production monitoring, execution tracing, custom criteria, and model and token cost tracking at the agent level.
More news
IBM adds self-hosted deployment for Bob development platform
NVIDIA launches Open Agent Safety Platform for AI-agent containment
SAP begins phased availability of Joule Studio agent tools