Public records show four MCP SSRF fixes; researcher claims fifth
Public records show related MCP server-side request-forgery fixes at Google, Weaviate, France's DINUM and Tangerang City. Researcher Syed Anas Mohiuddin identifies JPMorgan as a fifth case, but no public remediation record was found.
Public patches and advisories document related server-side request-forgery fixes in Model Context Protocol implementations at Google, Weaviate, France’s DINUM and Tangerang City’s government. Independent security researcher Syed Anas Mohiuddin identifies JPMorgan Chase as a fifth case. The reviewed material, however, includes no public JPMorgan advisory, CVE or patch.
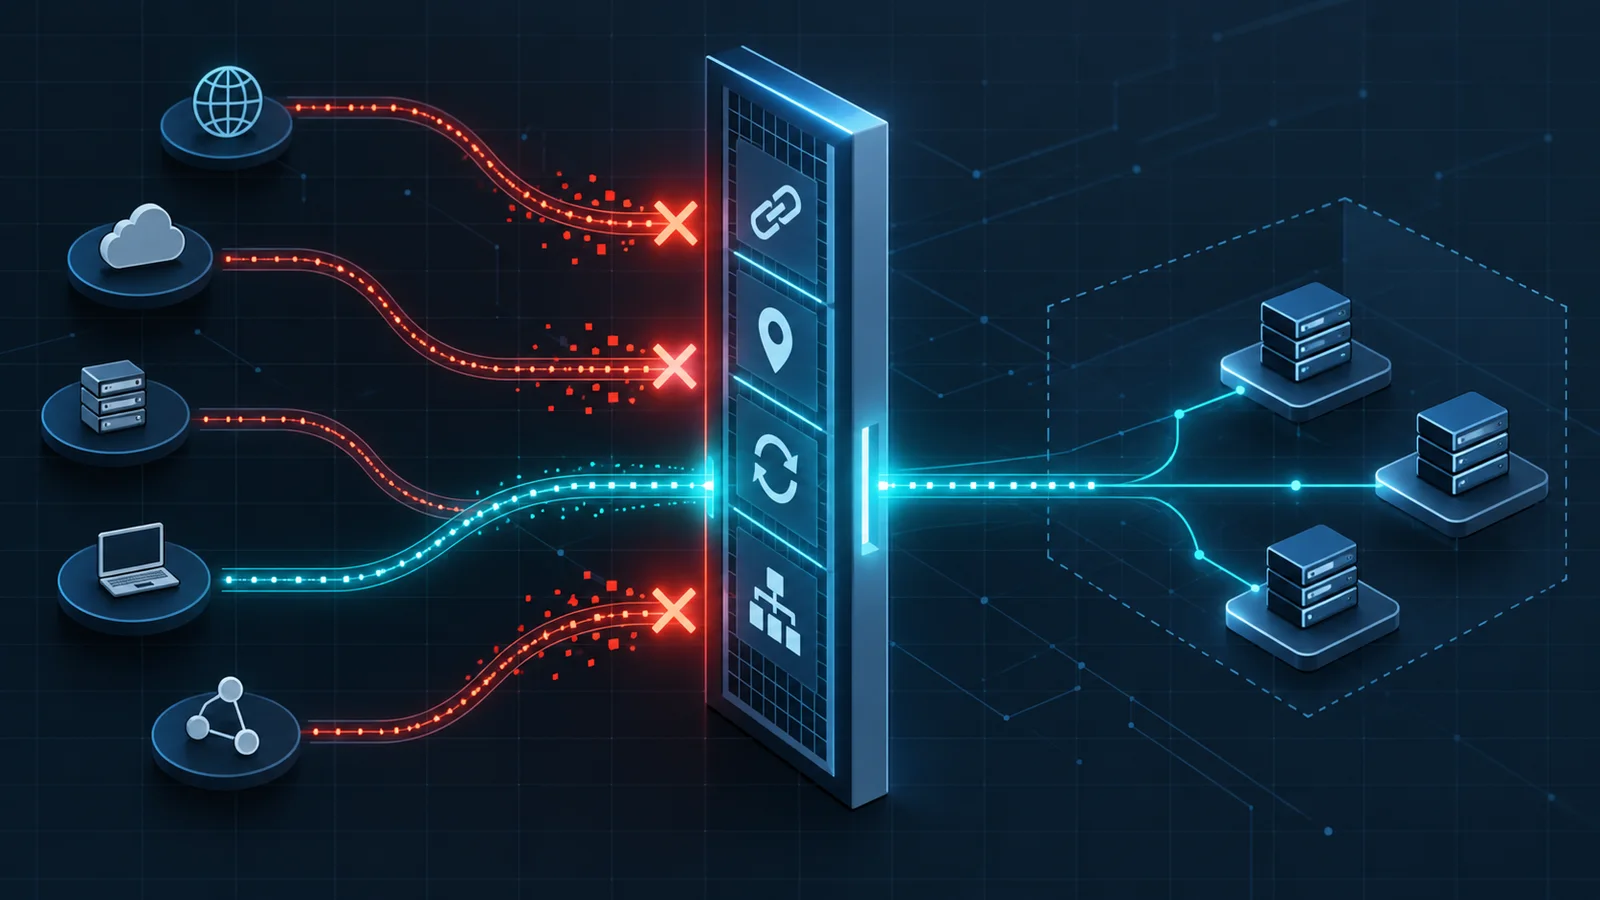
The four documented fixes add checks on where MCP-connected software may send requests. That matters when agents delegate work through MCP because a tool argument passed from one agent can become a network destination used by another system.
If the downstream boundary does not validate that input, attacker-influenced arguments can steer an authenticated server toward an internal service, a cloud-metadata address or an unintended external host. The records establish repeated validation failures in several implementations. They do not prove Mohiuddin’s broader claim that MCP or multi-agent architectures share a single structural flaw.
Google’s security record for CVE-2026-14540 says mcp-toolbox versions 0.3.0 through 1.4.0 did not adequately restrict redirects or validate target IP addresses in generic HTTP components. A crafted path parameter could redirect a request to an internal or arbitrary external endpoint. Published July 31, the advisory rates the issue high at 8.0 under CVSS 4.0.
Google merged its fix on June 18 and released mcp-toolbox 1.5.0. The patch added an SSRF guard, checks for connections and redirects, DNS-rebinding defenses, configurable address-range controls and validation of base URLs before use.
Weaviate said an unvalidated apiEndpoint in its Google-backed modules could redirect an outbound request and its attached Google credentials to an arbitrary host. Version 1.39.3 validates those values, while the accompanying code change restricts endpoint, region and location settings to Google API hosts. Weaviate rated the issue high at CVSS 7.1. On October 1, it said it had requested a CVE, which was still pending.
France’s data.gouv.fr MCP server fetched a producer-controlled documentation URL that could resolve to loopback, private-network or cloud-metadata destinations, including after a redirect. DINUM merged a patch on September 4 that limits requests to HTTP or HTTPS, validates destination IPs when connecting, rechecks redirects, blocks proxy use and rejects local or private destinations in the hosted service. No public CVE or vendor severity rating was found for that issue.
Tangerang City’s Wazuh MCP server checked literal private and reserved IP addresses but did not resolve hostnames before passing them to curl. It also followed redirects without validating each new destination. INFOKOM-KI published a high-severity advisory on September 3 and identified commit 2bbfe12 as the patch. The advisory lists no CVE.
Mohiuddin identifies JPMorgan as the fifth organization in his account. Because the reviewed material includes no public JPMorgan advisory, CVE or patch, the article does not independently characterize the reported flaw or claim that a fix was deployed.
Rapid7 fixed a separate boundary-validation problem, not another SSRF case. Bulk Export MCP versions 0.2.5 through 0.6.1 inserted an unvalidated export_id into a GraphQL query; version 0.6.2 parameterized the value. Rapid7’s public record says the issue remained within the operator’s authenticated API scope and rates it 2.7 under CVSS 3.1. Weaviate said it had no indication that its issue had been exploited.
More news
Meta patches Muse setting that let local malware hijack the AI agent
Nolla opens Utah pilot for AI-generated acne prescriptions
Wikimedia attributes unauthorized edits and heavy traffic to OpenAI agents