Microsoft broadens Sovereign Cloud controls across three deployment models
Microsoft is broadening sovereignty controls across its public cloud, customer-operated Azure Local environments and partner-run national clouds, with capabilities at different stages of availability, from external key management to disconnected AI workloads.
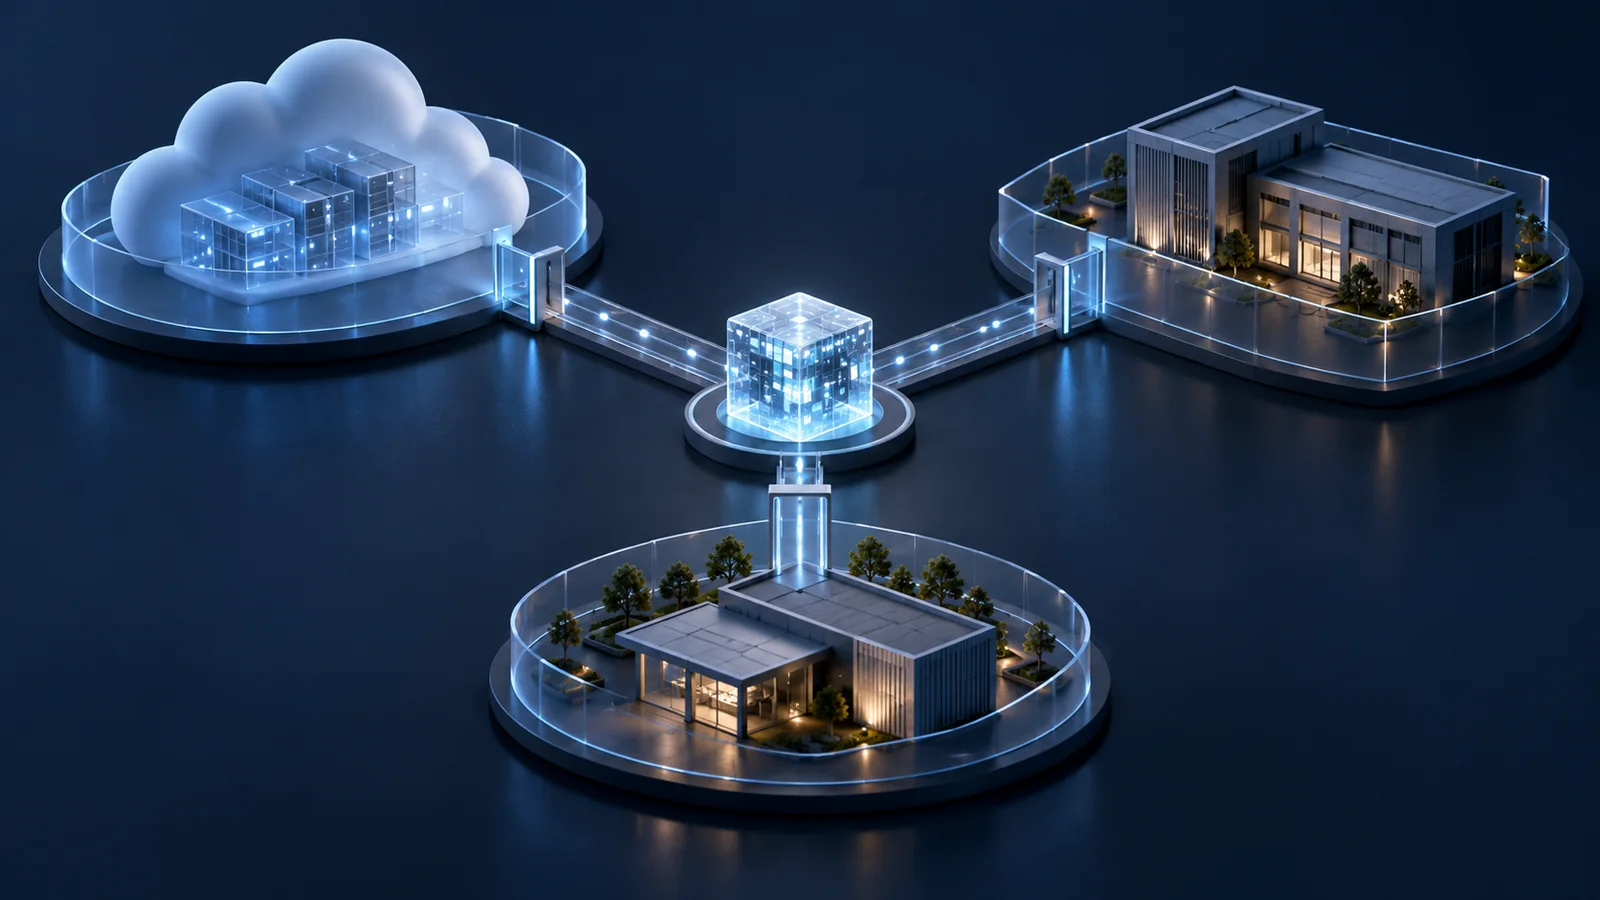
Microsoft has expanded its Sovereign Cloud framework across three deployment models, giving governments and regulated organizations more ways to place and control cloud and AI workloads in Microsoft-operated, customer-operated or locally partnered environments.
Customers can mix Sovereign Public Cloud, Sovereign Private Cloud and the Sovereign Partner Ecosystem by workload. The newly detailed controls are at different stages of availability: some are generally available, others are in public or limited preview, and Azure Local multitenancy remains planned without a release date.
For workloads staying in Microsoft’s public cloud, Sovereign Control Panel will enter public preview at Microsoft Ignite, the company said. The Azure portal interface is designed to show an organization’s sovereignty posture, apply controls, flag gaps and risks, and assess workload dependencies and portability.
Microsoft is also rolling out two access controls for customers in the European Union and European Free Trade Association. Data Guardian adds oversight by an unnamed, trusted EU partner when qualifying Microsoft engineers remotely access in-scope production systems. Production Touch Ledger is launching in phases with tamper-evident records of that access and the actions performed. Microsoft did not provide a country-by-country rollout schedule for either control.
Now generally available, External key management for Azure Managed HSM lets a customer or trusted third party keep a key-encryption key in hardware outside Microsoft’s infrastructure. Supported encryption-at-rest operations are routed through an externally operated proxy. Azure Confidential Clean Rooms, which Microsoft says can limit exposure of underlying data during approved multiparty analysis, is in limited preview.
The private-cloud option centers on Sovereign Private Cloud, which supports connected and disconnected operations on customer-controlled infrastructure. The ability to move workloads from connected to disconnected operation is entering public preview. SQL Server on Azure Local is generally available for both modes, while DocumentDB and Blob Storage on Azure Local are entering public preview.
Microsoft said Foundry Local will become generally available at Ignite for local model inference and agentic retrieval over enterprise data in connected or disconnected Azure Local environments. GitHub Enterprise Local is also due to become generally available at Ignite as a validated GitHub Enterprise Server appliance on Azure Local, with GitHub Copilot able to use locally hosted models for inference. Microsoft 365 Local integration is in preview for approved customers, and confidential virtual machines on Azure Local are generally available. Planned Azure Local multitenancy is intended to separate resources and governance across tenants sharing infrastructure, but Microsoft gave no preview or release date.
The third route is the National Partner Cloud model: physically and logically isolated environments operated by local entities and personnel under national compliance frameworks. Microsoft named Bleu Cloud in France and Delos Cloud in Germany as examples.
Microsoft’s own documentation characterizes customer-controlled Azure Local and private deployments as offering more control over hardware, software, data, location and management. It also says they do not match its hyperscale public cloud in cost efficiency, scalability, pace of innovation, security or reliability. Neither those comparisons nor the company’s broader claims about improved security, resilience and business continuity were supported by independent testing or outcome data in the opened sources.
External key custody can also transfer operational risk. Microsoft’s documentation says it provides no end-to-end Microsoft service-level agreement for the external proxy or hardware security module, and the configuration does not support geo-replication or Secure Key Release. It can add latency, places availability and maintenance responsibilities on the customer, and is not currently available in Azure Government or Azure China.
More news
Microsoft disrupts EvilTokens, citing 12,000 compromised inboxes
Researchers find Meta Muse share links in passive DNS
GMO links ARTEX to infrastructure targeting Japanese companies