AWS outlines Tata Elxsi's production IRIS safety platform
AWS has outlined how Tata Elxsi says its production IRIS platform filters industrial camera feeds at the edge, sends selected images and metadata to AWS, runs computer-vision models, then correlates detections before issuing safety alerts. The account's performance, incident-reduction and cost figures are company-reported and have not been independently verified.
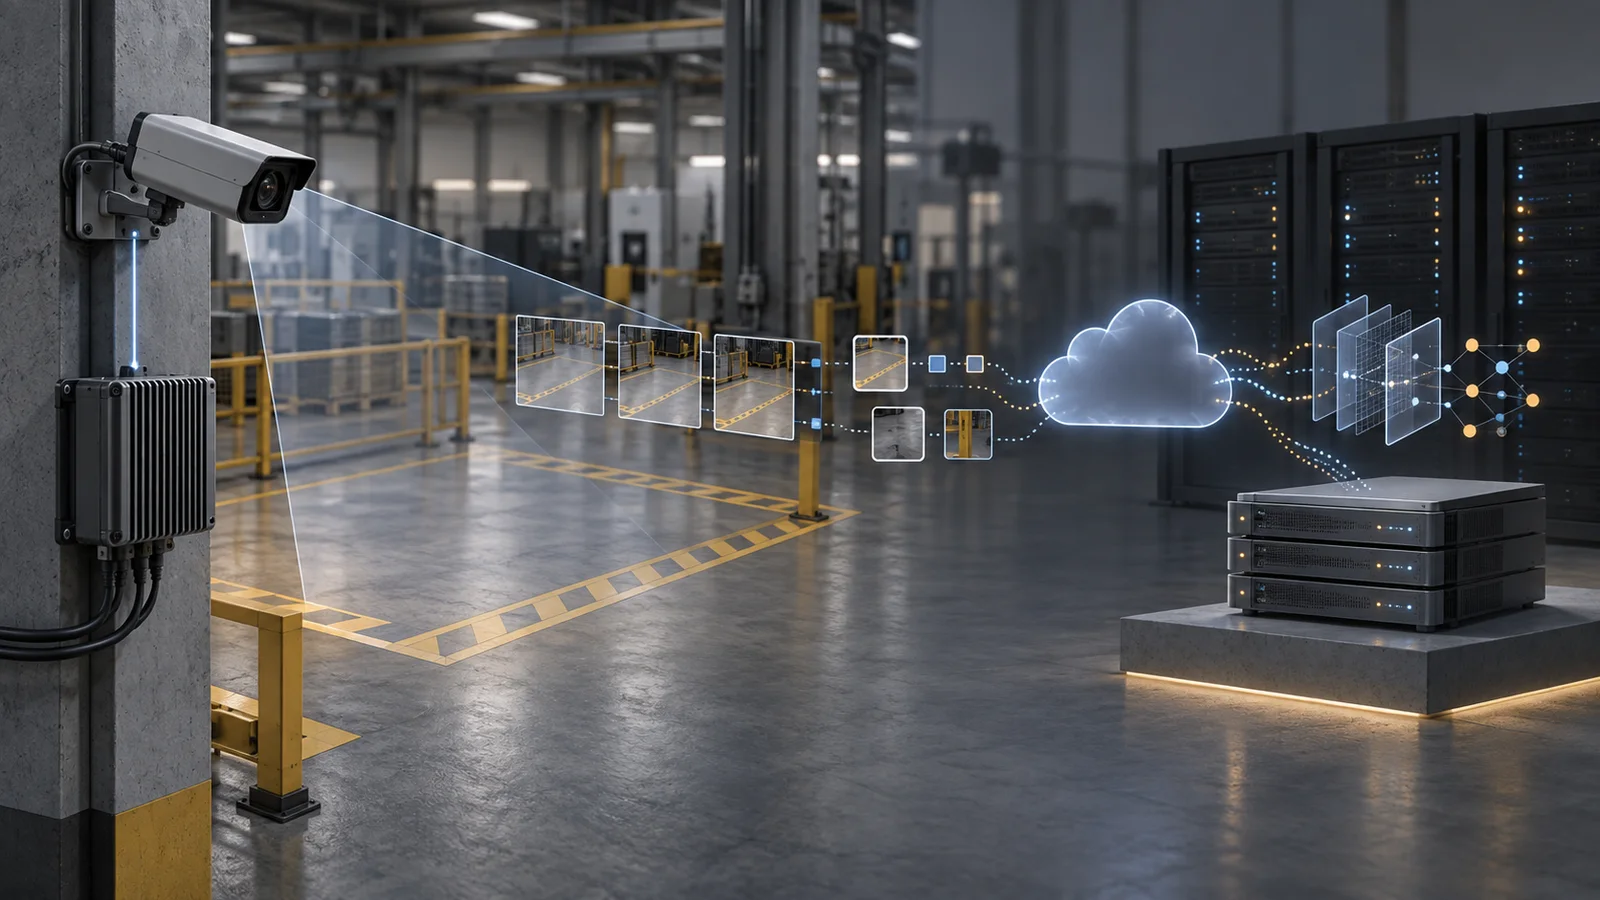
AWS has detailed how Tata Elxsi built IRIS, a production edge-to-cloud system that filters industrial camera feeds on site, streams event metadata to AWS, runs computer-vision inference and correlates detections before issuing safety alerts. The design is intended to cut the volume of video sent to the cloud while retaining images and context for potential safety events.
AWS says the deployment runs in its Asia Pacific (Mumbai) Region to meet data-residency requirements and stay close to customer facilities in India. Neither AWS nor Tata Elxsi names a customer or deployment site in the technical account, and the disclosed topology has not been independently audited.
At each facility, AWS says GPU edge servers running AWS IoT Greengrass connect to cameras through RTSP or ONVIF. The servers sample 2–5 frames per second, apply motion filtering and a lightweight first-pass model, then send selected frames to Amazon S3. Kinesis records carry the corresponding S3 object key, camera, plant, zone and synchronized timestamp instead of continuous video. AWS attributes to Tata Elxsi a roughly 70–80% reduction in frames sent to the cloud and says each event is smaller than 1 KB; both figures are company-reported and not independently verified.
Amazon Kinesis Data Streams carries that metadata and the resulting events in on-demand mode. AWS documentation says on-demand mode manages shards and capacity automatically, but it does not validate IRIS’s workload. AWS attributes to Tata Elxsi production throughput of 2,000–5,000 events per second, bursts of about 15,000 events per second and event-ingestion latency below 200 milliseconds at the 95th percentile. Those performance figures are company-reported and not independently verified.
AWS says IRIS handles inference through separate Amazon SageMaker real-time endpoints for models that detect personal protective equipment, restricted-zone entry, worker-safety patterns and vehicle or equipment proximity. The disclosed methods include YOLOv8, SlowFast-based action recognition, tracking, geofencing and monocular depth. AWS says the endpoints use ml.g5.xlarge instances with at least two instances per endpoint, while an SQS queue smooths bursts and requests are grouped into micro-batches of 4–8 frames. AWS’s SageMaker documentation confirms that endpoints can be registered as scalable targets, but it does not verify this deployment. AWS attributes to Tata Elxsi about 40–60 inference requests per second per endpoint and per-frame inference latency below 300 milliseconds at the 95th percentile; those company-reported performance figures are not independently verified.
AWS says Lambda functions keep short-lived state in DynamoDB records and correlate detections over configurable windows of 30 seconds to 5 minutes. The scoring considers location, zone criticality, event frequency and duration, severity and historical behavior. AWS says a Tata Elxsi internal benchmark estimated that this step reduced spurious alerts by 40–50% compared with passing detections through directly. The company-reported figure has not been independently verified.
Lambda and Step Functions then de-duplicate, classify and escalate events, according to AWS. The disclosed policy targets an alert within 5 seconds for critical events and within 10 seconds for high-severity events, delivered through dashboards, email, SMS, webhooks or mobile push. Those are company-reported operating targets, not independently verified measurements of achieved end-to-end latency.
AWS says S3 retains confirmed-event frames for one year before archival and removes frames with no detection or a below-threshold detection after seven days. AWS also says training, inference and analytics are separated across AWS accounts, with customer-managed encryption keys, TLS 1.2 or later, least-privilege access, private networking, CloudTrail and GuardDuty. These retention and security settings are part of the vendor’s disclosed design and have not been independently verified in customer deployments.
The post says about 80% of IRIS training data is annotated production material collected under customer agreements and 20% is synthetic data for rare cases. Low-confidence predictions enter human review, a pattern also used in a separate AWS-based AI pipeline for medical claims review, although the applications and evidence are distinct. AWS attributes to Tata Elxsi held-out validation results including 94.2% precision, 91.8% recall and 92.7% mAP@0.5 for PPE detection; 96.1% precision and 93.4% recall for restricted-zone detection; and a post-correlation false-positive rate below 3%. Those proportions and model-quality figures are all company-reported and not independently verified; AWS did not publish the underlying datasets, sample sizes or evaluation protocol.
AWS also says Tata Elxsi reports unsafe-condition detection in under 5 seconds, continuous 24x7 audit coverage, a 15–20% reduction in recordable safety incidents during the first six months, about a 30% reduction in manual-surveillance operating cost and support for hundreds of concurrent streams at each site. Every performance, safety-outcome, scale and cost figure in that account is company-reported and not independently verified. The post does not provide an incident denominator, exposure-hour adjustment, cost baseline, site count or calculation method.
A separate Tata Elxsi case study describes an IRIS deployment for an unnamed British heavy-equipment manufacturer using live IP-camera feeds, deep-learning models, alerts and a centralized dashboard. The case supports the existence of a production industrial-safety deployment, but it does not say the customer used the AWS architecture described in the September 22 post. No named customer, customer representative, deployment contract, independent benchmark or third-party technical audit was identified for the architecture and results AWS described.
More news

xAI launches Team Bots for shared workflows

AWS adds xAI’s Grok 4.7 to Amazon Bedrock

OpenAI adds $5 million and up to $5 million in credits to Lenfest AI program
