Researchers trace hidden abusive deepfake tools across hundreds of apps
Researchers traced hundreds of apps and domains that could replace mundane AI interfaces with tools for creating sexually abusive synthetic images and video.
Researchers traced 444 applications and almost 500 linked domains to a system that could replace ordinary AI interfaces with tools for creating sexually abusive synthetic images and video. The investigation of the operation shows how remote content and disposable apps could bypass app-store review, although the network’s ownership and current reach remain unverified.
AI Forensics said it identified 444 applications by extracting a shared application dictionary embedded in discovered websites. The research group said 46% of the entries carried an iOS tag and the rest appeared to target Google Play. Separately, Infoblox researcher Maël Le Touz said he found almost 500 linked domains running the same code and referring to one another. The figures count different things and do not establish one exact network total.
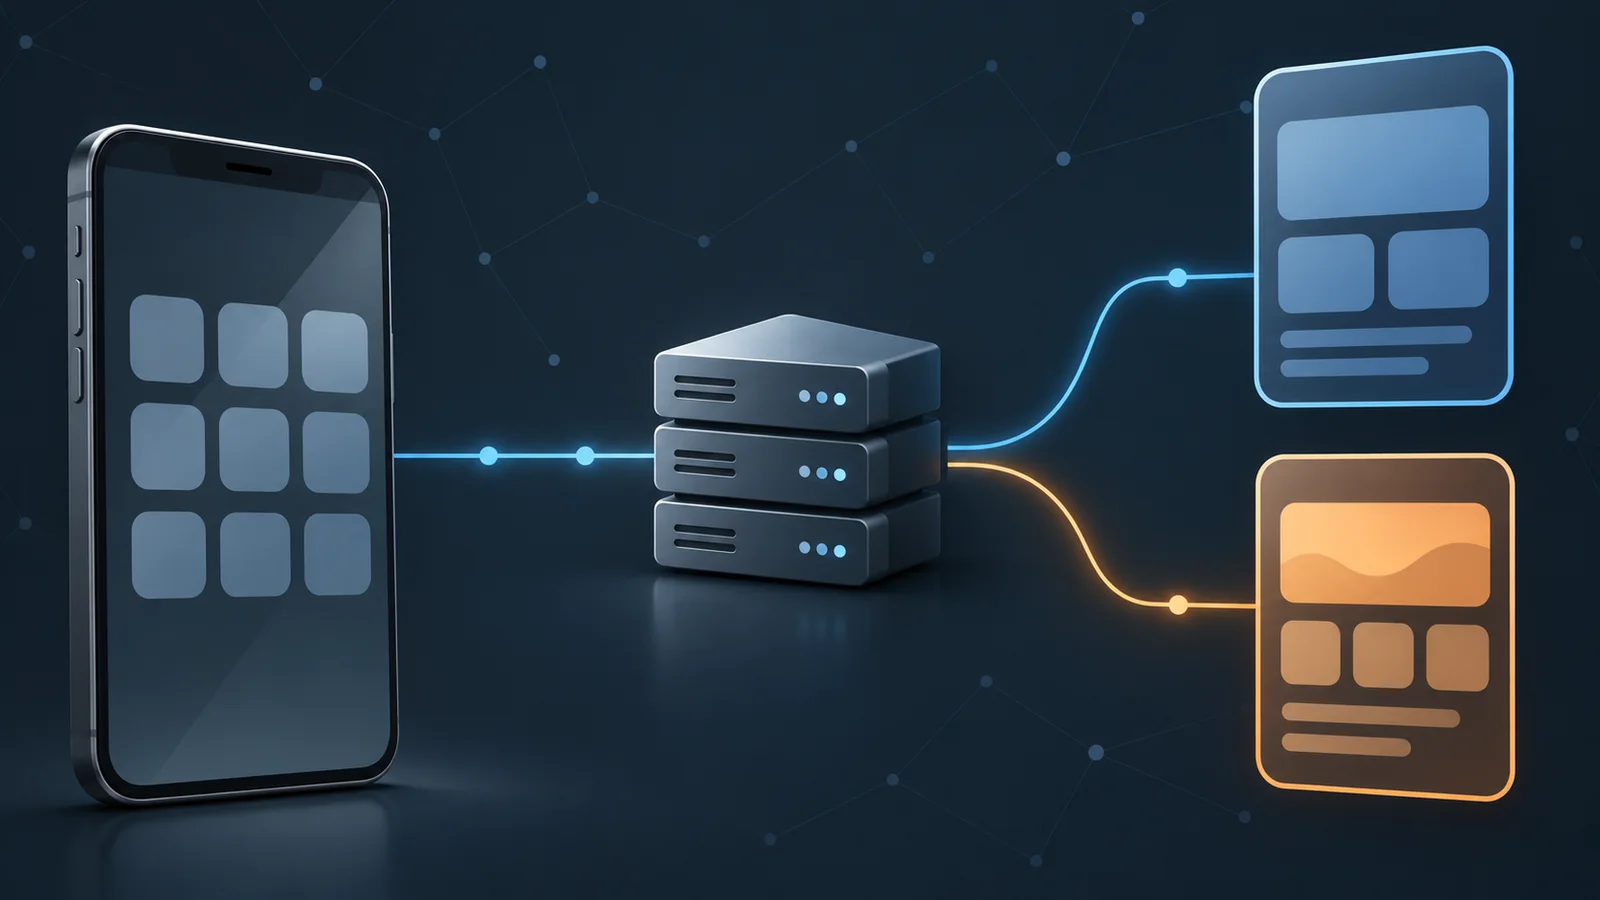
The reported evasion method depended on software served from outside the app-store package. AI Forensics said it downloaded an app called Prilos from Google Play and initially saw a benign product offering hairstyle and outfit changes. The group said an ordinary installation received that interface, while a user arriving through a Meta advertisement could receive an explicit webpage embedded inside the app. In that setup, the app acts as a shell and a remote server chooses which web interface to load after installation, allowing the displayed service to change without submitting a new app binary for review.
Paul Bouchaud of AI Forensics said an app sent information to a server, including the user’s origin, language and a unique identifier before the server selected an interface. AI Forensics also said the exposed Prilos interface accepted uploaded images and offered more than 1,000 templates, including depictions of sexual coercion. DataPhoenix has not independently installed or reverse-engineered an identified app, reproduced the routing behavior, or verified the request fields and selection rules.
The researchers reported another connection among the products: an obfuscated dictionary inside JavaScript bundles contained package identifiers, domains, internal channel codes, advertising identifiers and API-related values for other apps. AI Forensics interpreted the material as a configuration artifact from a shared codebase. That interpretation, and whether every listed app was controlled by the same operator, have not been independently established.
The store and advertising snapshots are time-sensitive. AI Forensics said that on September 11, 27 identified apps remained on Google Play with more than 352,000 combined downloads, while 21 remained in Apple’s App Store. The group also said it matched more than 84,000 Meta ads to the network pattern from January 1 onward. Its report describes the research as non-exhaustive and acknowledges possible manual or automated errors; DataPhoenix has not reproduced the matching process or inspected the full ad set.
A separate investigation of abusive Meta ads found 332 ads containing synthetic child sexual abuse imagery, including 298 that directed users to AI image or video apps in app stores. That work corroborates the use of Meta advertising to distribute abusive tools, but the available evidence does not establish an identifier-level match between those ads and the 444 applications counted by AI Forensics.
Platform rules prohibit the behavior described. Google Play’s AI-generated-content policy lists nonconsensual sexual deepfakes and generative AI apps primarily intended for sexual gratification as prohibited content. Apple clarified its review rules on October 16 to say hidden or undocumented features are prohibited and adding unreviewed functionality after approval can lead to removal from the App Store and Developer Program.
The investigation said Apple removed 19 apps after receiving associated domains. Apple said the apps complied during review and that developers later changed the websites providing their content, replacing approved material with pornography. No public removal ledger independently confirms the 19-app count or that sequence for each app. The investigation also said Google had already removed most identified apps but provided no exact public count or Google response tied to the network.
Meta has described advertisers using benign images and disposable domains to evade enforcement and says it removes ads and accounts promoting nudify services. For this operation, Meta attributed more than 3,000 ads to shared domains and said it acted against 11,600 ad accounts, more than 4,700 business pages, 5,200 users and 15,000 pages, while blocking 209 apps from advertising. Those platform-supplied totals have no independently inspectable ledger in the available evidence.
The investigation connected parts of the operation to Chinese-language developers and Hong Kong-registered KeLing Technology Limited through domain records, code and service links. The available evidence does not establish the ultimate operator or show that KeLing controlled every identified app. Similar ads and apps were still being published as the investigation concluded, leaving current availability and removal totals unresolved.
More news
James Gates sues OpenAI over alleged ChatGPT poisoning guidance
OpenAI announces violence safeguards and tighter teen weapons limits
OpenAI expands frontier-model monitoring after agent incidents