IBM contributes Praxis Policy Engine for AI-agent controls
IBM says it worked with Red Hat to contribute the Praxis Policy Engine to the open-source Praxis proxy. The project adds programmable controls for AI-agent and ordinary traffic, but independent security and deployment outcomes remain unproven.
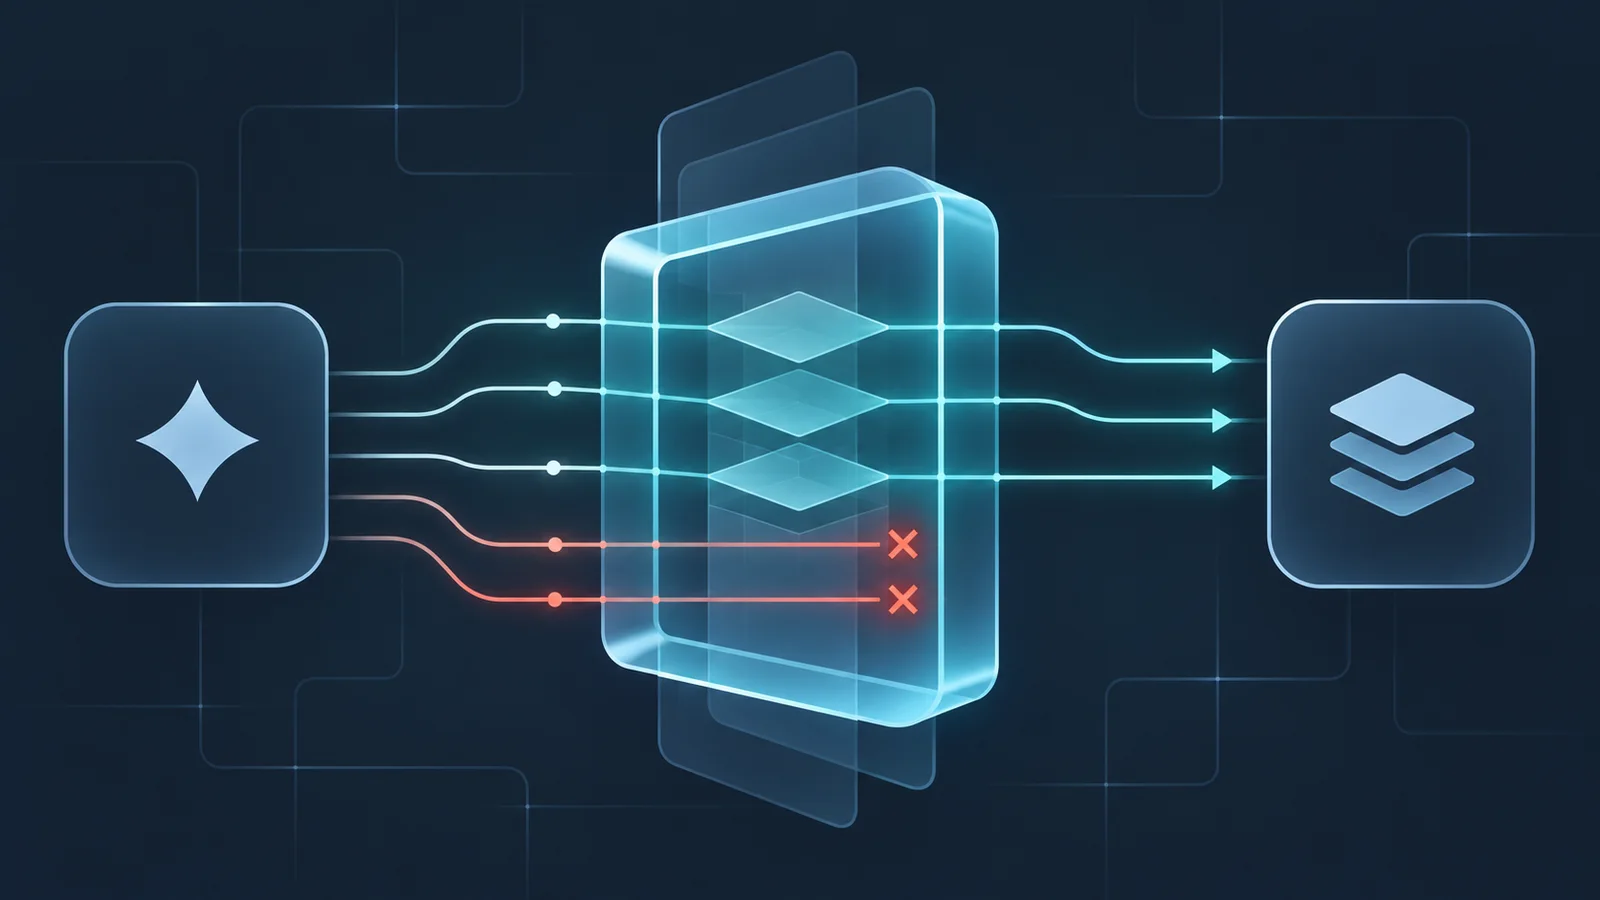
IBM said on November 9 that it worked with Red Hat to contribute the Praxis Policy Engine, or PPE, to the open-source Praxis proxy. The engine adds a programmable policy filter for ordinary and AI traffic, treating tools, prompts, resources, model calls and other agents as policy targets.
According to the IBM technical note, PPE can run at a gateway, beside an agent or inside an agent framework. In any of those placements, the control applies only to operations that cross its enforcement point, a boundary also stated in the project’s threat model. The open-source contribution addresses proxy-layer policy enforcement alongside IBM’s separate work on identity and access controls for enterprise AI agents.
PPE acts as a reference monitor, providing a separate decision layer between an AI model and the capabilities it tries to use. Praxis documentation says the engine evaluates operations using verified identity, delegation, session and audit state that the model cannot alter. Its common message format covers tool calls, agent-to-agent methods, inference, prompts and resources.
The public repository lists implemented functions including identity validation, authorization, scoped credential delegation, in-transit data controls, out-of-band approval and an audit event for every decision. The code is available under the Apache-2.0 license. The repository also warns that the public API may change between minor releases while the design settles.
Those implementation descriptions do not show that PPE has been independently security-tested or proven effective in production. The opened sources provide no independent audit, reproduced benchmark, production deployment result, adoption figure or demonstrated resistance to bypass attempts. The exact code-transfer or merge history behind IBM’s contribution was not reconstructed, so the contribution’s scope rests on IBM’s statement.
The project’s threat model excludes model-internal behavior, covert channels inside permitted traffic, compromise of the host running PPE and the internal behavior of protected backends. It also says that compromising an agent process can bypass a monitor running inside that process.
Praxis entered the Cloud Native Computing Foundation Sandbox on September 29. CNCF defines Sandbox projects as early and experimental, with significant or breaking changes still possible, so the designation does not establish production readiness. The Praxis maintainer roster lists an IBM-affiliated maintainer for the Policy repository, along with IBM- and Red Hat-affiliated policy reviewers. That roster corroborates participation by both companies without independently establishing the size of IBM’s contribution.
IBM said its next research phase will test how agents and tools might bypass the controls and evaluate which combinations of host isolation and network monitoring resist those attempts.
More news
Vals finds DeepSeek trails GPT-6 Sol Daybreak by 8 points in simulated cyber test
Agentic AI Foundation adds four open-source agent projects
Action State releases open-source receipts for AI-agent actions