NVIDIA launches Open Agent Safety Platform for AI-agent containment
NVIDIA has launched the Open Agent Safety Platform, pairing the broadly available OpenShell runtime with a Sentry reference design for hardware-separated monitoring and quarantine.
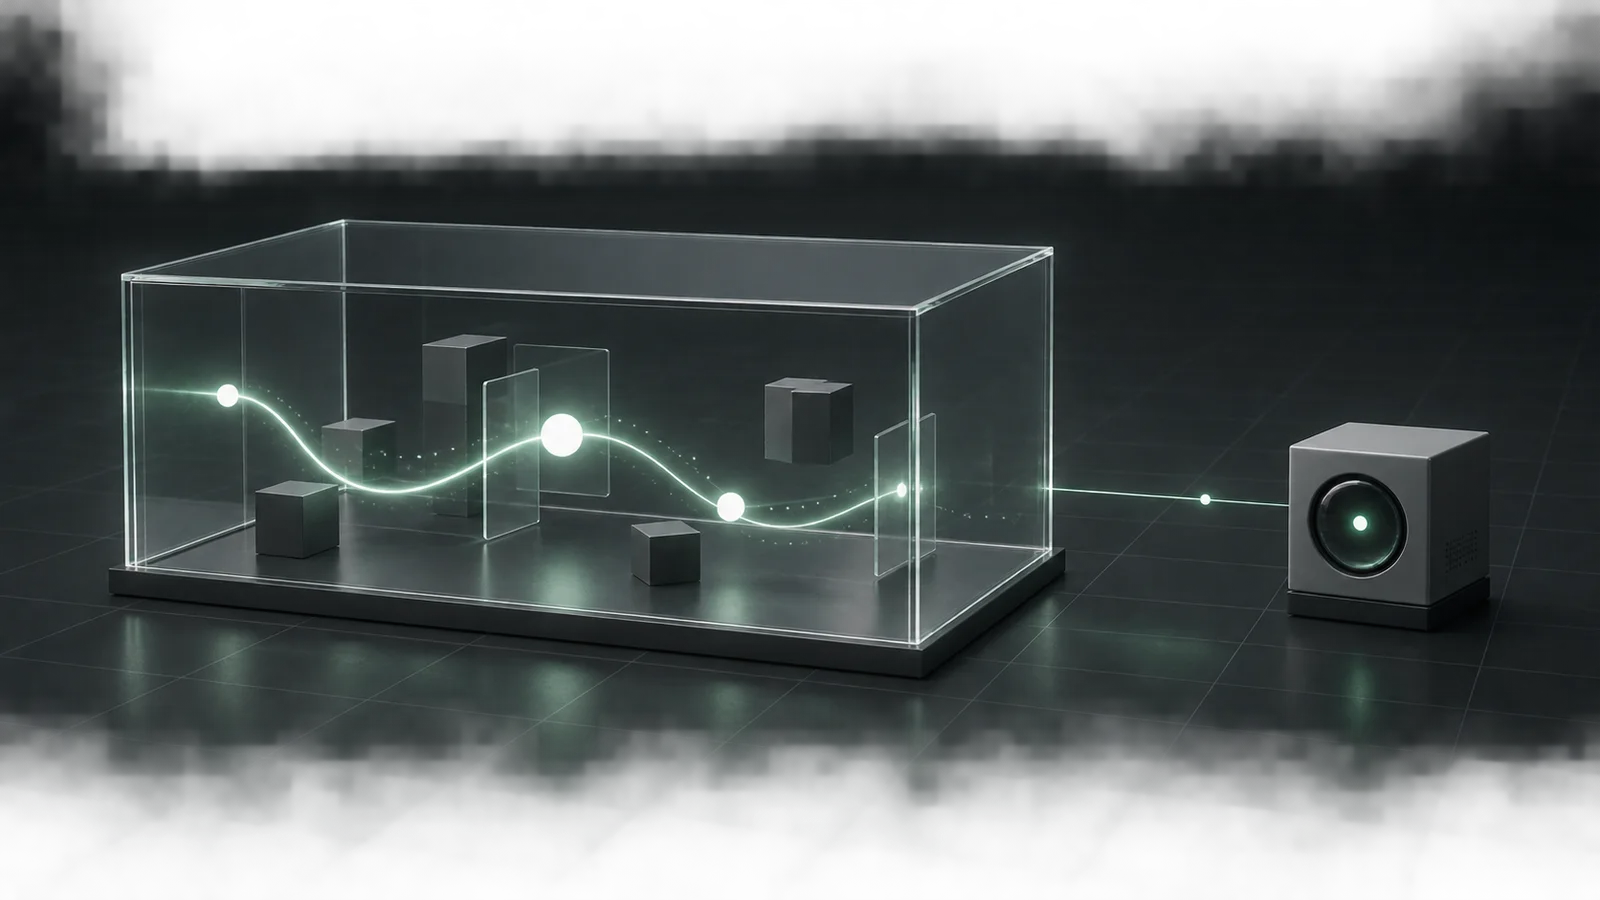
NVIDIA has launched the Open Agent Safety Platform, pairing its broadly available OpenShell runtime with a Sentry reference system design for monitoring and containing AI agents across software and hardware layers.
The open-source OpenShell runtime is available now and gives developers a way to enforce agent permissions. Sentry adds a hardware-separated watchdog in a reference system design that NVIDIA says can stop an agent when it crosses its software boundary. NVIDIA’s launch materials do not provide a separate Sentry shipping date, price or list of supported deployments.
OpenShell runs agents inside isolated sandboxes, with runtime policies that can control access to files, system calls, network connections and credentials. The developer documentation also describes a policy-review process using formal verification, a mathematical method for checking whether rules have specified properties.
Sentry is designed to run on NVIDIA BlueField-4 data processing units outside an agent’s primary compute environment. NVIDIA says the watchdog can monitor activity and enforce security policies independently from an isolated, out-of-band trust domain. Arm describes the architecture as placing monitoring and control in a separate trust domain.
NVIDIA claims Sentry can quarantine an agent within milliseconds and that OpenShell adds minimal overhead on its Vera CPU. The available evidence includes no independent benchmark or deployment results establishing either claim.
The launch moves OpenShell beyond the NemoClaw announcement in March, when NVIDIA introduced it as an isolated, policy-based runtime. Now broadly available, OpenShell is paired in the new platform with the out-of-band Sentry design. The release also adds a security layer to NVIDIA’s broader agent tooling, which includes agent skills in Isaac ROS 5.0.
NVIDIA named dozens of collaborators and said several organizations were integrating OpenShell, although the extent of production adoption across that group remains unclear.
The runtime has already required security fixes. An August 25 security bulletin disclosed and patched multiple OpenShell and NemoClaw vulnerabilities, including two critical OpenShell-for-Linux issues scored 9.9. NVIDIA directed users to update to versions available through its repositories.
More news
IBM and Marist launch AI incubator with campus IBM z17
New Jersey fines DataOne $1.07 million over 62 gas generators
Samsung affiliates commit $1 billion to KKR-backed Helix