Databricks opens Private Network Gateway public preview on Azure
Databricks has opened Private Network Gateway in public preview on Azure, giving supported serverless workloads one managed route to private resources and controlled egress. AWS remains in private preview.
Databricks has opened Private Network Gateway in public preview on Azure. The managed networking feature remains in private preview on AWS.
For Azure customers, the gateway gives supported Databricks serverless workloads one managed route into customer-controlled networks for private resources and outbound traffic. The release advances the feature from the private preview Databricks announced in June. AWS release notes listed the AWS private preview on August 24. The October announcement does not give an AWS public-preview date.
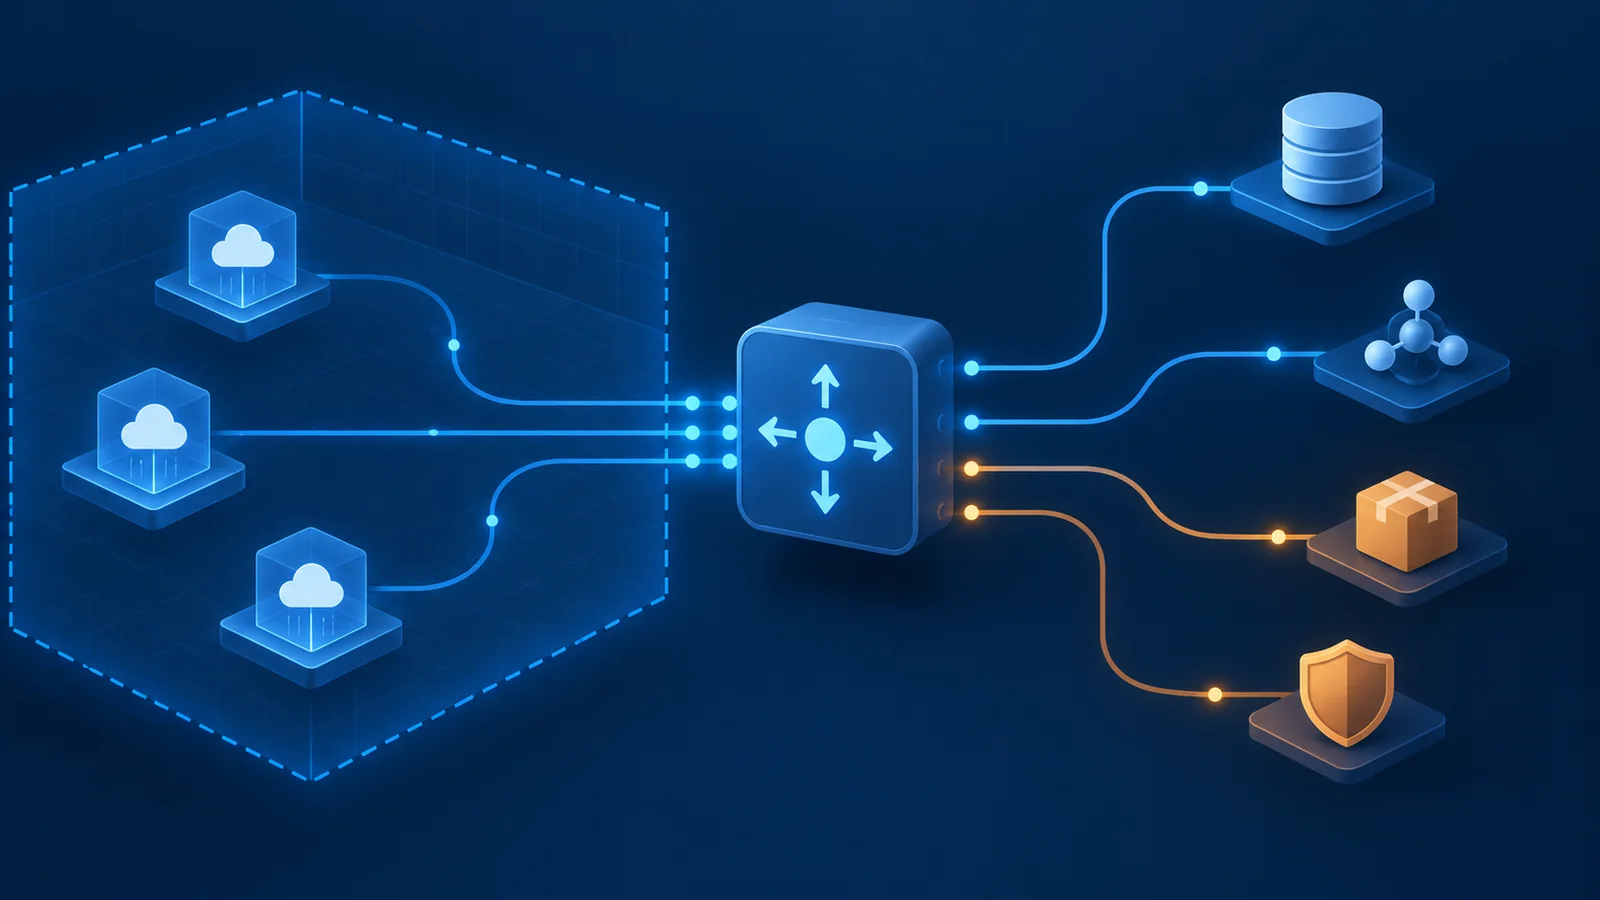
On Azure, an account administrator delegates a virtual-network subnet to Azure Databricks, then creates the gateway inside an existing account-level Network Connectivity Configuration, or NCC. Once the NCC is attached to workspaces, supported serverless products can use the gateway to reach resources available through that subnet. Those resources can include systems on connected networks reached over ExpressRoute or VPN.
Databricks says it creates and operates the gateway, leaving customers without gateway virtual machines to deploy, patch or scale. Customer route tables, network security groups, DNS resolvers and security appliances still determine what is reachable beyond the delegated subnet.
The Azure documentation describes two traffic modes. SPECIFIC_DESTINATIONS sends only listed DNS names through the gateway and leaves other traffic on existing routes; Microsoft recommends this mode for most uses. ALL_TRAFFIC sends remaining outbound serverless traffic through the gateway, though more-specific paths such as Private Link and Azure service endpoints retain priority. Destinations intended for the gateway in ALL_TRAFFIC mode must also be allowed by the serverless egress network policy.
Databricks lists four main uses: ingesting from supported private databases with Lakeflow Connect, allowing AI agents to call private Model Context Protocol services, installing Python libraries from private PyPI, Artifactory or Nexus repositories, and routing serverless egress through a customer firewall for inspection and logging. That network-level database path differs from catalog-level integrations such as Databricks’ Workday Data Connect federation in Unity Catalog.
The company says the service enforces workspace-level access controls before traffic leaves. The gateway complements rather than replaces Private Link. Azure Blob Storage traffic continues to use the service-endpoint path and cannot be overridden by the gateway.
During the Azure preview, bandwidth tiers are 10, 30, 50 and 100 Gbps. Each NCC supports at most two gateways, while each gateway supports at most two DNS resolvers and 100 destinations.
Private Network Gateway is not billed during the Azure preview, according to Microsoft. Azure Databricks plans to charge for it later but has not disclosed pricing or a billing start date. Databricks says Google Cloud support is in development but has not given an availability date.
More news
Databricks details Proteus harness for shape-specialized GPU kernels
Apple adds MLX distributed inference across Mac Studio systems
CoreWeave credit risk hits record as Huang says Nvidia backstop is not needed